SAML | IDP Certificate through CURL | Community
Skip to main content
Veera_kandregul
Level 2
Feb 19, 2018 3:06 AM UTC
Solved

SAML | IDP Certificate through CURL

Hi All,

Am looking into options on how to configure SAML on our AEM instances, especially uploading truststore and keystore.

From the documentation, we understand that we can go to admin console and manually upload the certificates, but they are manual steps and biggest issue is the truststore alias is random number which is restricting us to put SAML config in source control.

Can you let us know if there is any other option to upload the truststore and keystore into AEM instances, say through CURL?

Also, is there a way to predefine the truststore alias key?
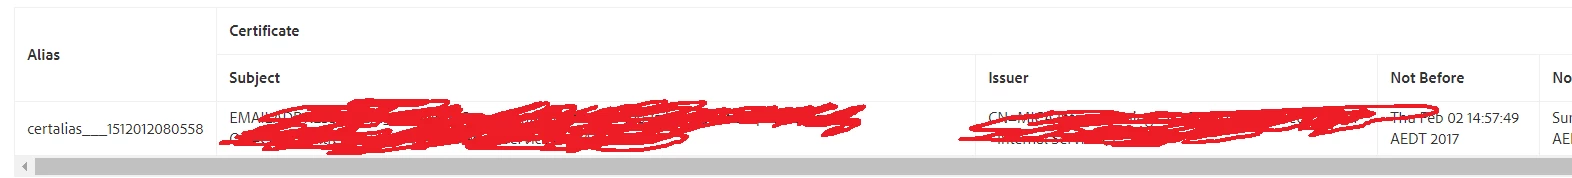
Note: Tried below solution but not working in 6.2

Providing TrustStore and KeyStore from content package

This post is no longer active and is closed to new replies. Need help? Start a new post to ask your question.
paulorosAccepted solution
New Participant
Mar 8, 2018 11:11 PM UTC

Hi Veera,

The only option I found so far to more predictably package the truststore is:
  1. create the truststore on one instance (manually)
  2. add the IDP certificate manually
  3. write down the certificate alias
  4. create the SAML config based on that alias
  5. create a package with /etc/key, /etc/truststore, /home/users/system/authentication-service

When you deploy this package on another instance it should have the same certificate ID in the new instance.

If you find a better/different way, let me known.

Regards,

Paul

6 replies

smacdonald2008
Level 10
Mar 9, 2018 2:13 PM UTC

New article out soon too - but this is done manually.

Scott's Digital Community: Integrating SAML with Adobe Experience Manager

Translate
paulorosAccepted solution
New Participant
Mar 8, 2018 11:11 PM UTC

Hi Veera,

The only option I found so far to more predictably package the truststore is:
  1. create the truststore on one instance (manually)
  2. add the IDP certificate manually
  3. write down the certificate alias
  4. create the SAML config based on that alias
  5. create a package with /etc/key, /etc/truststore, /home/users/system/authentication-service

When you deploy this package on another instance it should have the same certificate ID in the new instance.

If you find a better/different way, let me known.

Regards,

Paul

Translate
Veera_kandregul
Level 2
Mar 5, 2018 2:39 AM UTC

Bumping up to the top again,

Any pointers pls?

Translate
Veera_kandregul
Level 2
Feb 23, 2018 4:29 AM UTC

Hi All,

Any pointers pls?

Translate
Veera_kandregul
Level 2
Feb 19, 2018 5:41 AM UTC

Hi Prateek,

Thank you for your comments.

We are creating new instances for every release, so the concept of 'apply once' and 'stays forever' wont apply for us.

Looking into ways how we can create trust store (with predefined alias) through non-manual steps, so that we can put those steps as part of stack creation.

Cheers,

Veera

Translate
prateekkumar1
Level 2
Feb 19, 2018 5:33 AM UTC

Hi Veena

The truststore alias is generated only once. You need to take it and add it in com.adobe.granite.auth.saml.SamlAuthenticationHandler.xml file against idpCertAlias property. You can then source control the xml file.

Please let me know if you need more information.

Translate