Update expired time for login-token cookie | Community
Skip to main content
John_Ky
Level 2
Jul 7, 2017 7:38 AM UTC
Solved

Update expired time for login-token cookie

Hi,

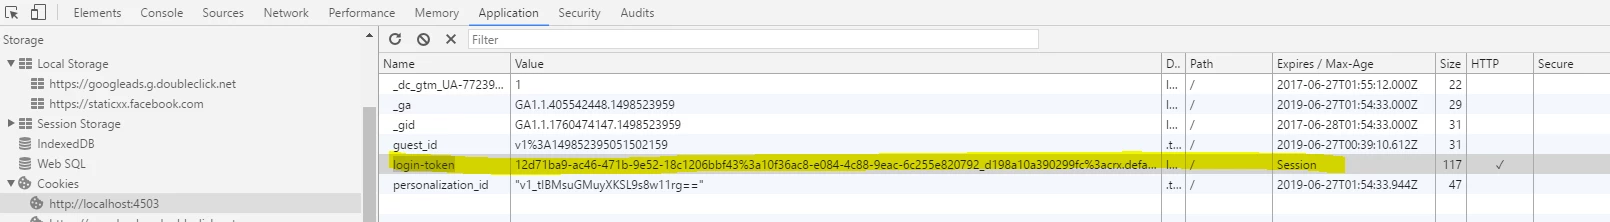
I am using AEM 6.1 and having a problem which login-token cookie is a session cookie and will automatically be cleaned when browser closed.

My question is, could we update the expired time for that cookie so it will be retaining for a period of time on client site.

I did a lot of searches but they were only mentioning to how to configure the server site token (under "/home/users/usernode").

Furthermore, if my thing is possible to do, does it cause any security problem?

Is it a good practise to do it by apache mod_header (override the set-cookie response header)?

Regards,

Thanh
This post is no longer active and is closed to new replies. Need help? Start a new post to ask your question.
John_Ky
John_KyAccepted solution
Level 2
Jul 14, 2017 4:34 AM UTC

Hi,

My solution: Because “login-token” cookie is from OTB Token Login Module of AEM, we cannot edit the Expired/Max-age from AEM site unless creating new login module. The easiest way is using Apache Http mod_header to override the “SetCookie login-token” of “Response header” of “authentication request”.

Area 1: Using Apache Http Mod_Header rewrite setcooke header of authentication response.

Add this line of code to apache configuration:

Header edit Set-Cookie ^(login-token.*)$ $1;max-age=99999999

Area 2: Configure Server site “Expire Session” to make expired time consistent with client cookie.

http://aemfaq.blogspot.com.au/2014/10/how-to-set-timeout-for-login-token.html

4 replies

John_Ky
John_KyAuthorAccepted solution
Level 2
Jul 14, 2017 4:34 AM UTC

Hi,

My solution: Because “login-token” cookie is from OTB Token Login Module of AEM, we cannot edit the Expired/Max-age from AEM site unless creating new login module. The easiest way is using Apache Http mod_header to override the “SetCookie login-token” of “Response header” of “authentication request”.

Area 1: Using Apache Http Mod_Header rewrite setcooke header of authentication response.

Add this line of code to apache configuration:

Header edit Set-Cookie ^(login-token.*)$ $1;max-age=99999999

Area 2: Configure Server site “Expire Session” to make expired time consistent with client cookie.

http://aemfaq.blogspot.com.au/2014/10/how-to-set-timeout-for-login-token.html

Translate
John_Ky
John_KyAuthor
Level 2
Jul 10, 2017 2:44 AM UTC

Hi Kautuk,

Thanks for your answer, those of your references were talking only about token configuration at server site. but My question was about client site cookie "login-token" (Session ID).

The authentication process is, AEM uses a cookie name "login-token" as a session ID which is stored on user's browser (Client site). For subsequent requests, AEM will use that cookie "session id" to query the session object under "/home/users/<usernode>/.token". Therefore "session expired time" is a property of node ".token" (Server site).

I am thinking of using Apache Http to rewrite the cookie.

Regards,

Thanh

Translate
kautuk_sahni
Employee
Jul 7, 2017 12:40 PM UTC
kautuk_sahni
Employee
Jul 7, 2017 12:39 PM UTC

See this :- FAQ: How to set timeout for login-token

// For AEM 6+ 

configure tokenExpiration at http://<host>:<port>/system/console/configMgr/org.apache.jackrabbit.oak.security.authentication.token.TokenConfigurationImpl

Also make sure to set Token Length otherwise will throw exception "org.eclipse.jetty.servlet.ServletHandler / java.lang.IllegalArgumentException: Invalid token ''"

More details on AEM6+ refer http://jackrabbit.apache.org/oak/docs/security/authentication/tokenmanagement.html

Source :- FAQ: How to set timeout for login-token

~kautuk

Translate
Kautuk Sahni